


The sovereign platform for autonomous exposure management.
Panop discovers internet-facing, cloud and internal assets, offensively tests what is exploitable, and ranks what to fix.
- +00:12discover1,247 assets mapped · 86 unknown
- +00:26validatepath: internet → staging → API → DB · 3 hops

One platform that sees your entire attack surface, every cloud, every vendor, every AI asset and tells your team exactly what to fix first. Continuously. Autonomously. Preemptively. From Switzerland.
From discovery to remediation, in real time, every day.
Panop continuously discovers, validates and prioritises exposure across cloud environments, external attack surfaces and third-party ecosystems, so teams see what matters before it becomes operational risk.
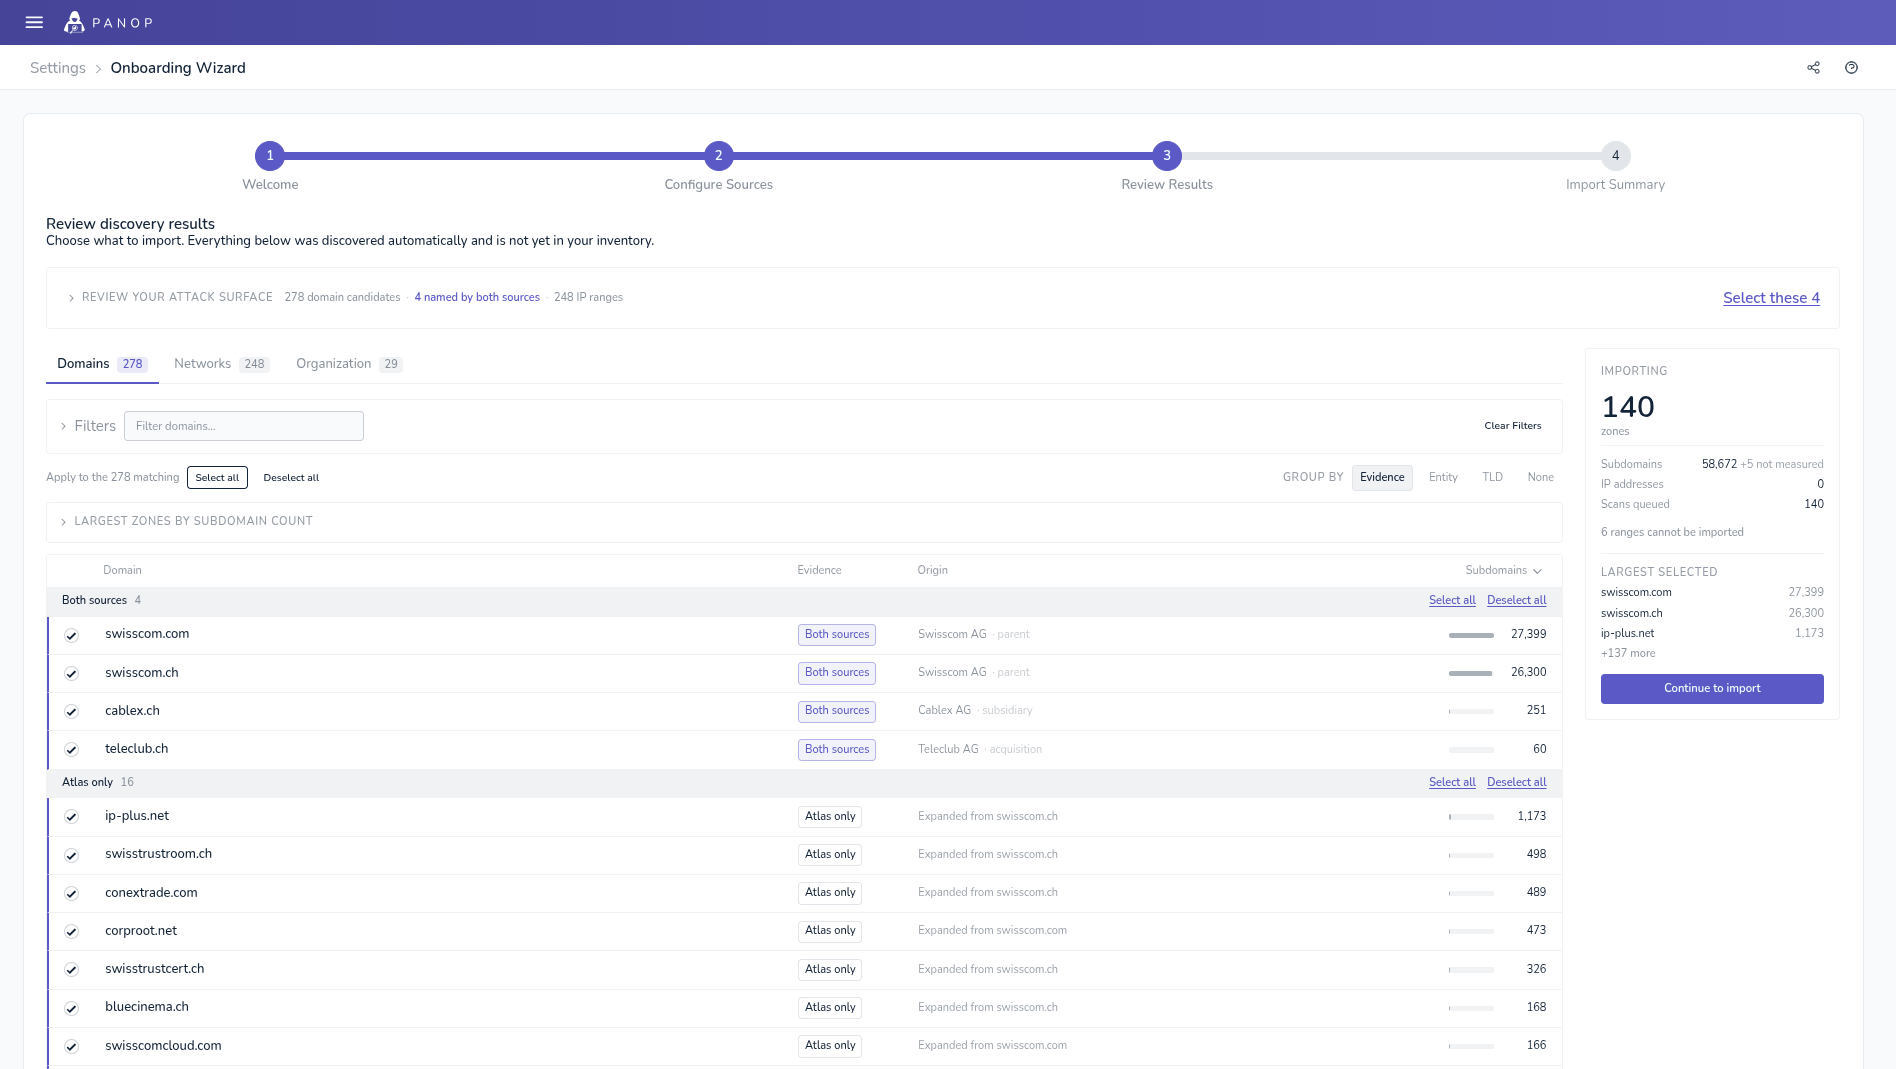
01 · Discovery
Seedless discovery. Every asset, every cloud.
See beyond your known attack surface.
Panop finds your attack surface the way attackers do. No asset lists, no setup, no limits. Every cloud environment, every vendor, every AI model your teams have deployed. Known and unknown.
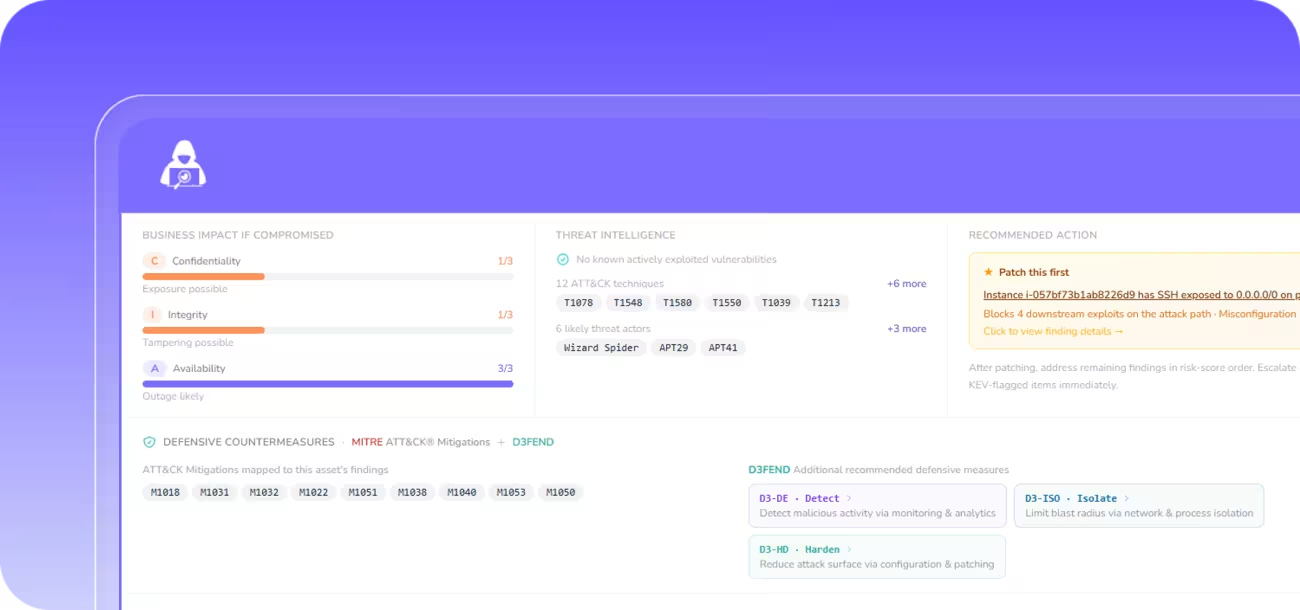
02 · Context
Business impact, not just asset inventory.
Exposure signals, connected to what they put at stake.
Panop scores exposures across cloud, on-premise, hybrid environments and third-party suppliers by what they put at stake for the business, not technical severity alone. Scores are weighted by data sensitivity, revenue dependency, regulatory exposure, blast radius and exploitable attack paths.
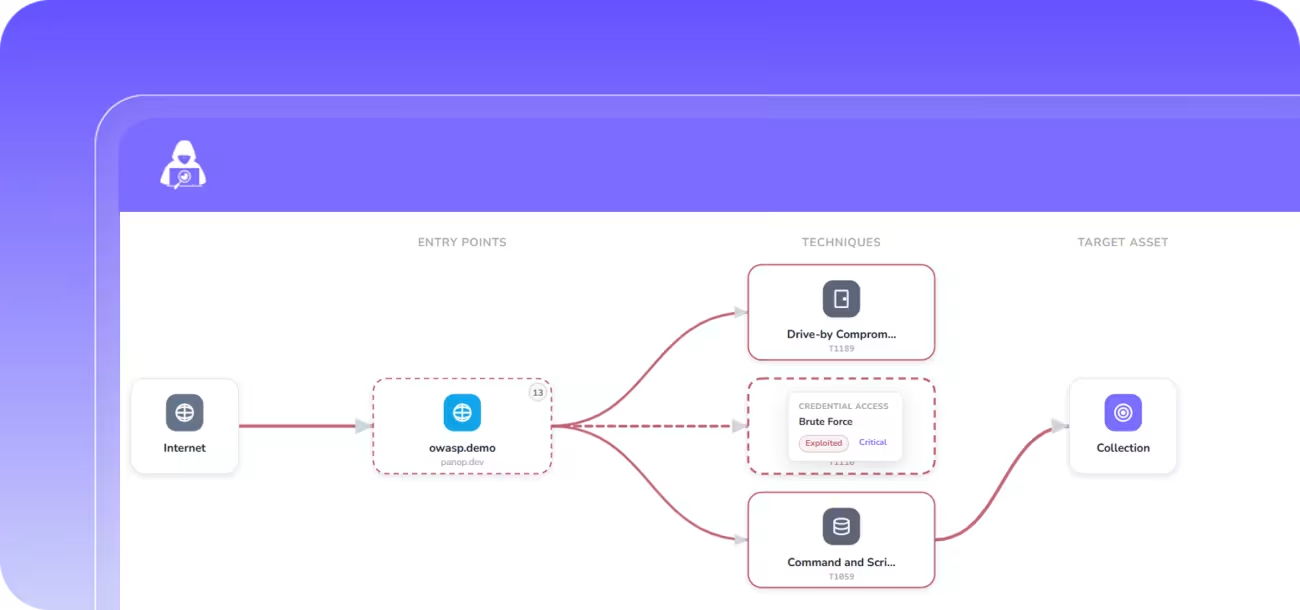
03 · Validation
Confirm what is actually exploitable.
Cut through noise. Reveal what’s real.
Not every finding is a real risk. Panop agents validate each exposure against real-world exploitability, separating theoretical issues from attack paths an adversary could chain into a breach today.
Autonomous offensive simulation, safe for production. Attack paths mapped from exposure to critical assets.
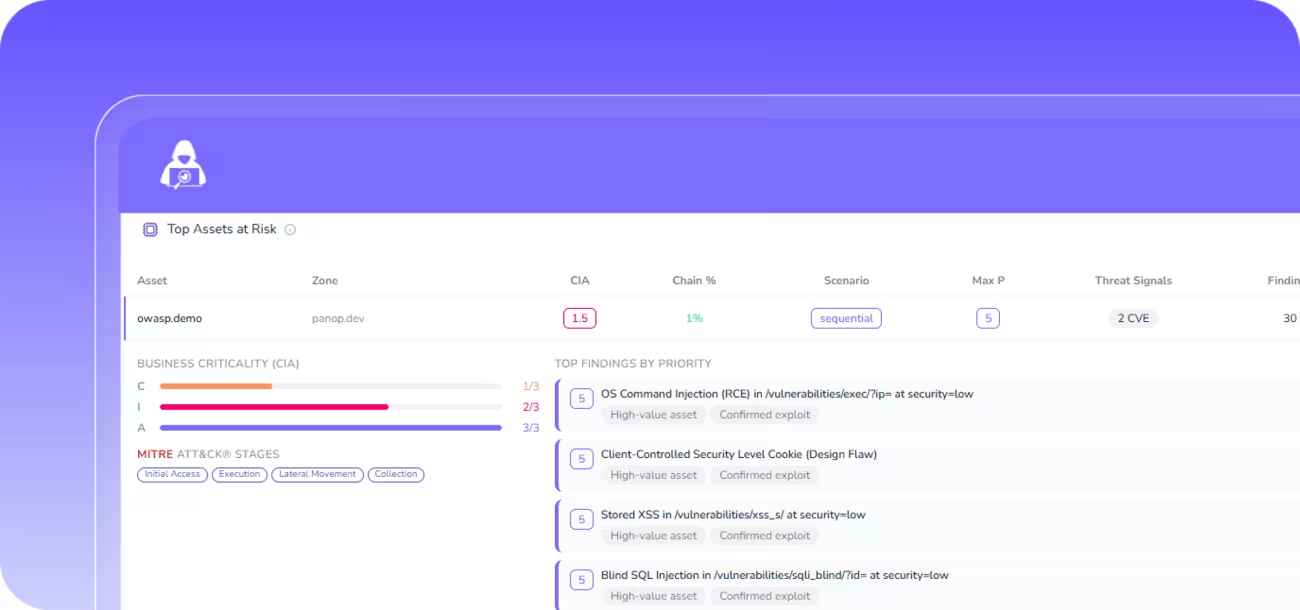
04 · Prioritisation
Your 10 actions for today.
Not all exposure is risk. Panop shows you which is.
Focus remediation where exposure creates the highest business and organisational impact.
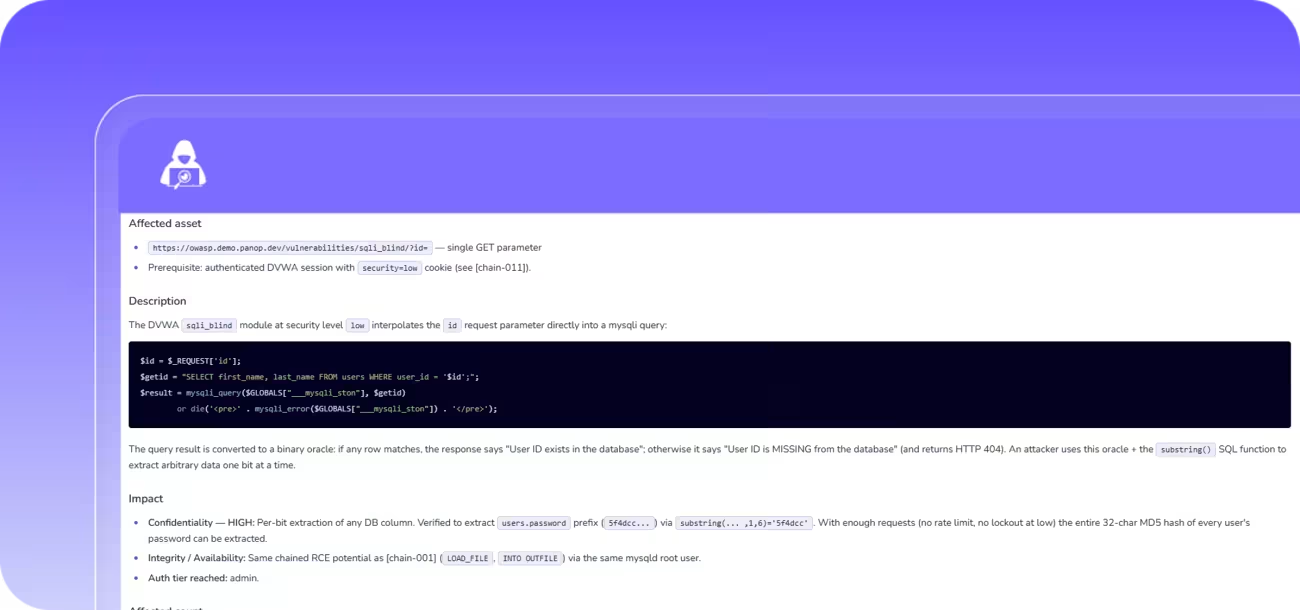
05 · Remediation
Fixes at machine speed.
Prioritised findings flow into the tools your teams already use.
Tickets open automatically in ServiceNow, Jira or your ITSM. Security and engineering work from the same ranked queue instead of trading spreadsheets and Slack handoffs.
Clarity that drives operational impact.
75%
Attack paths
Reduce propagation risk toward critical systems.
90%
Prioritisation
Accelerate remediation through risk-based prioritisation.
95%
Blind spots
Uncover previously unknown assets.
Your security data belongs to you. It stays in Switzerland.
Panop is built and operated in Switzerland, supported by Innosuisse Initial and Core Coaching and Trust Valley, and developed in partnership with leading Swiss AI research institutions. Your exposure intelligence, the most sensitive data your organisation generates, never crosses a border you have not explicitly chosen.
- Data residency
- Customer exposure data is hosted in Switzerland.
- Jurisdiction
- Panop SA, a Swiss company based in Crissier.
- Evidence mapped to
- NIS2
- DORA
- ISO/IEC 27001
- PCI DSS 4.0
- GDPR
- FINMA
- EU AI Act
- Sub-processors
- Published list
- Supported by
- Innosuisse Initial and Core Coaching · Trust Valley
Real use cases. Real impact.
Whether you’re prioritising risk, adopting cloud, testing security or governing AI, see how teams reduce uncertainty and focus on what matters.