


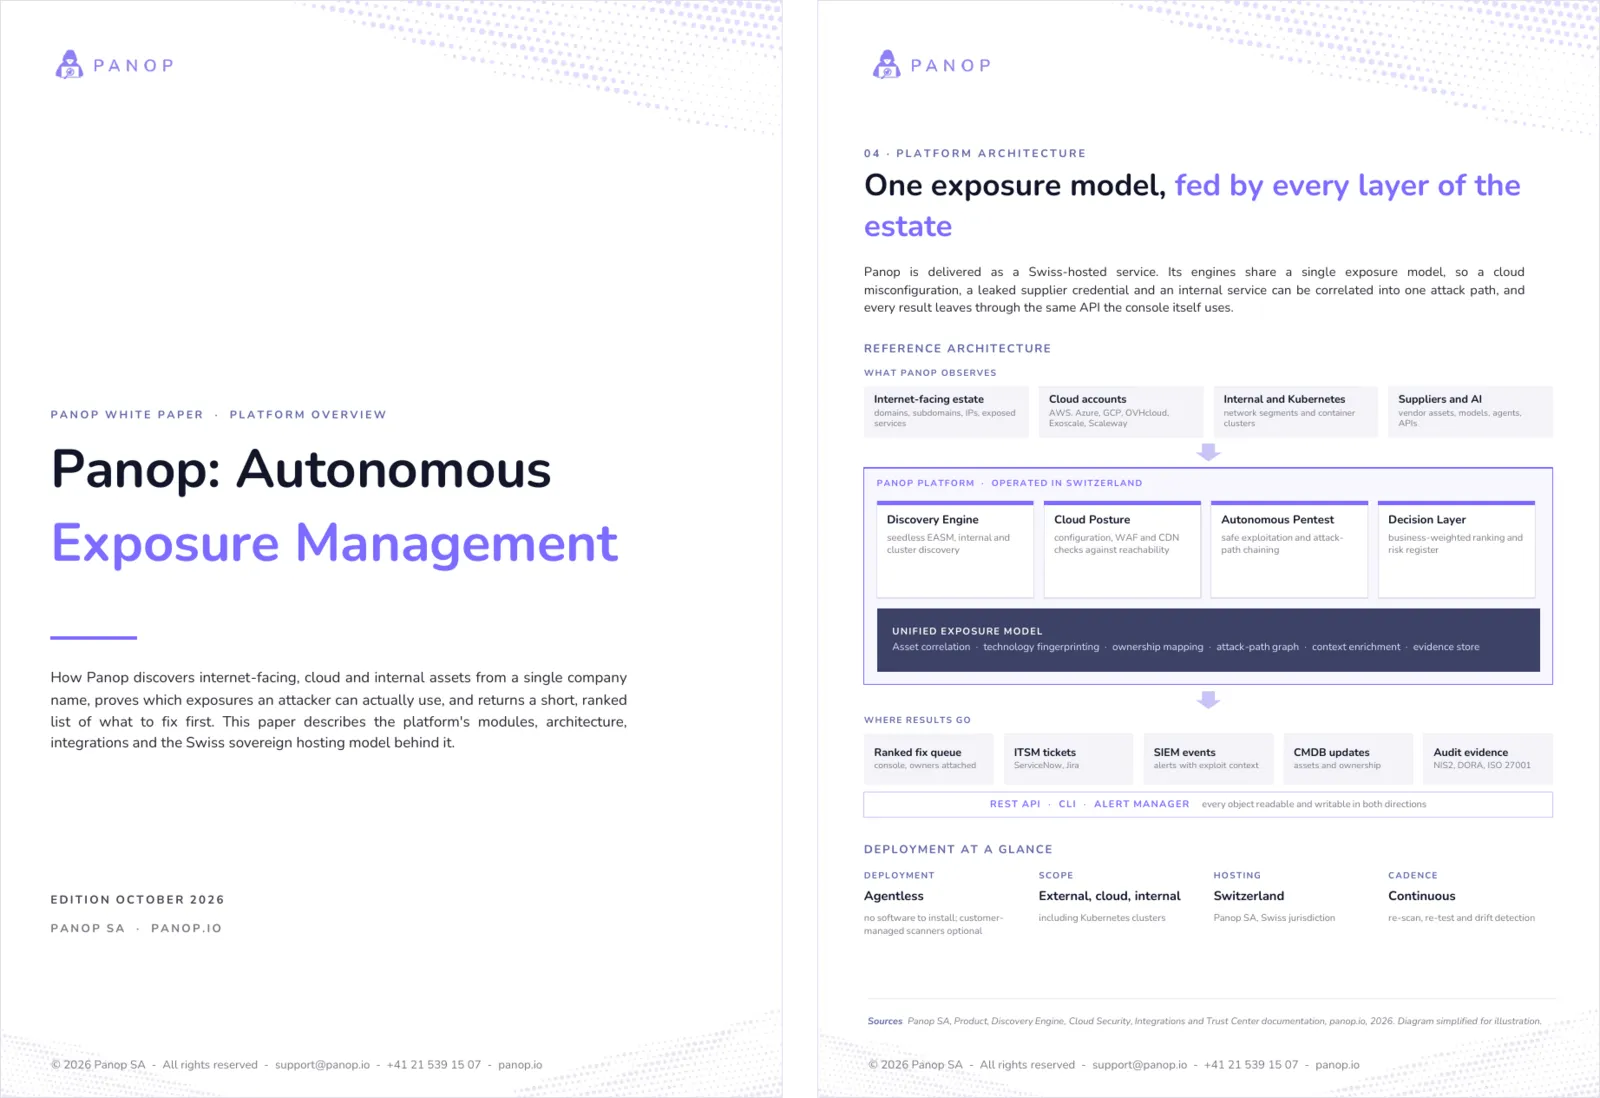
The Panop platform, in ten pages.
How Panop discovers internet-facing, cloud and internal assets from a single company name, proves which exposures an attacker can actually use, and returns a short, ranked list of what to fix first.
Inside the white paper:
- The four gaps current tooling leaves open, and the five stages that close them
- The reference architecture: one exposure model fed by every layer of the estate
- The modules: Discovery Engine, Cloud Security Posture, Autonomous Pentest, Decision Layer, AI-SPM and Third-Party Risk
- Integrations: REST API, CLI, Alert Manager and native ITSM, SIEM and CMDB connectors
- Security, Swiss sovereign hosting and the frameworks Panop maps evidence to
Download the white paper
PDF, 10 pages, October 2026 edition.